Ghidra
by National Security Agency
Ghidra Reverse Engineering Suite
About
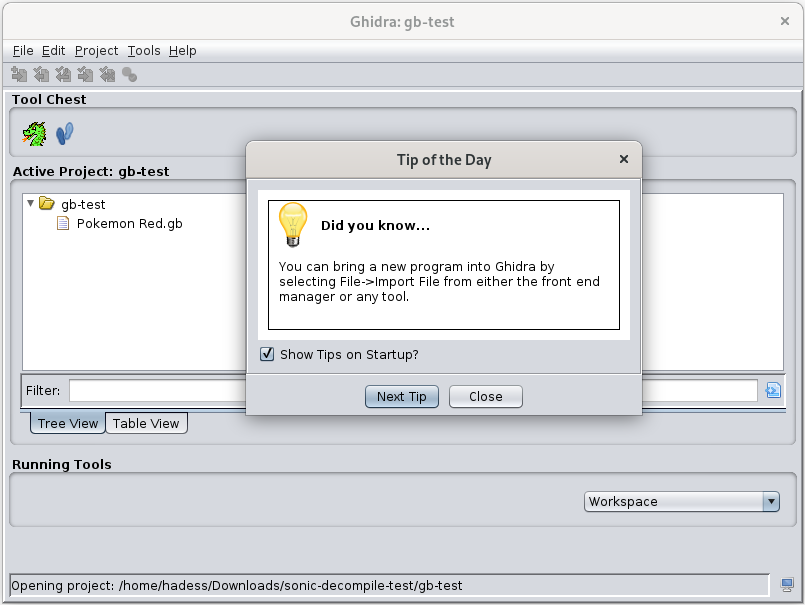
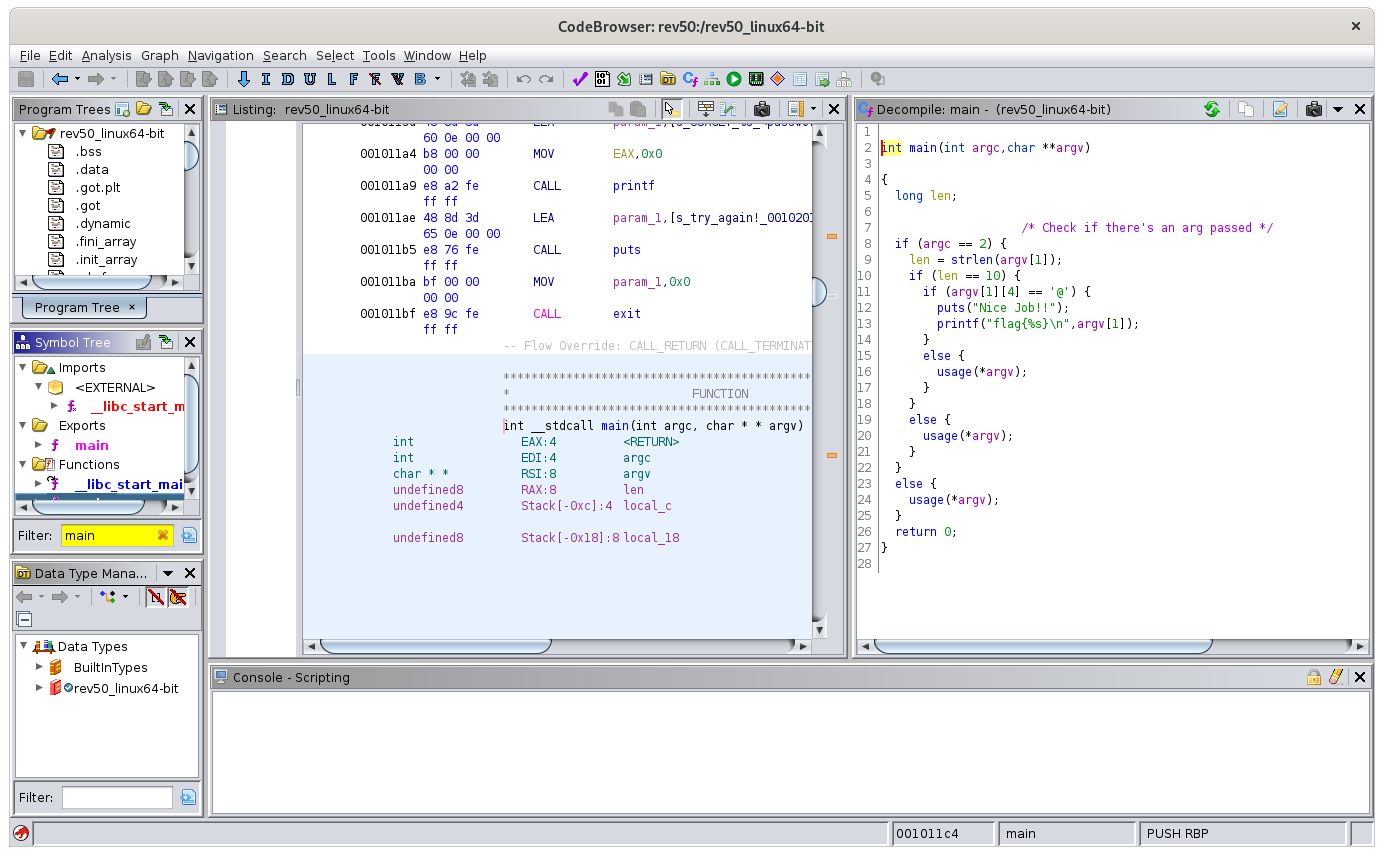
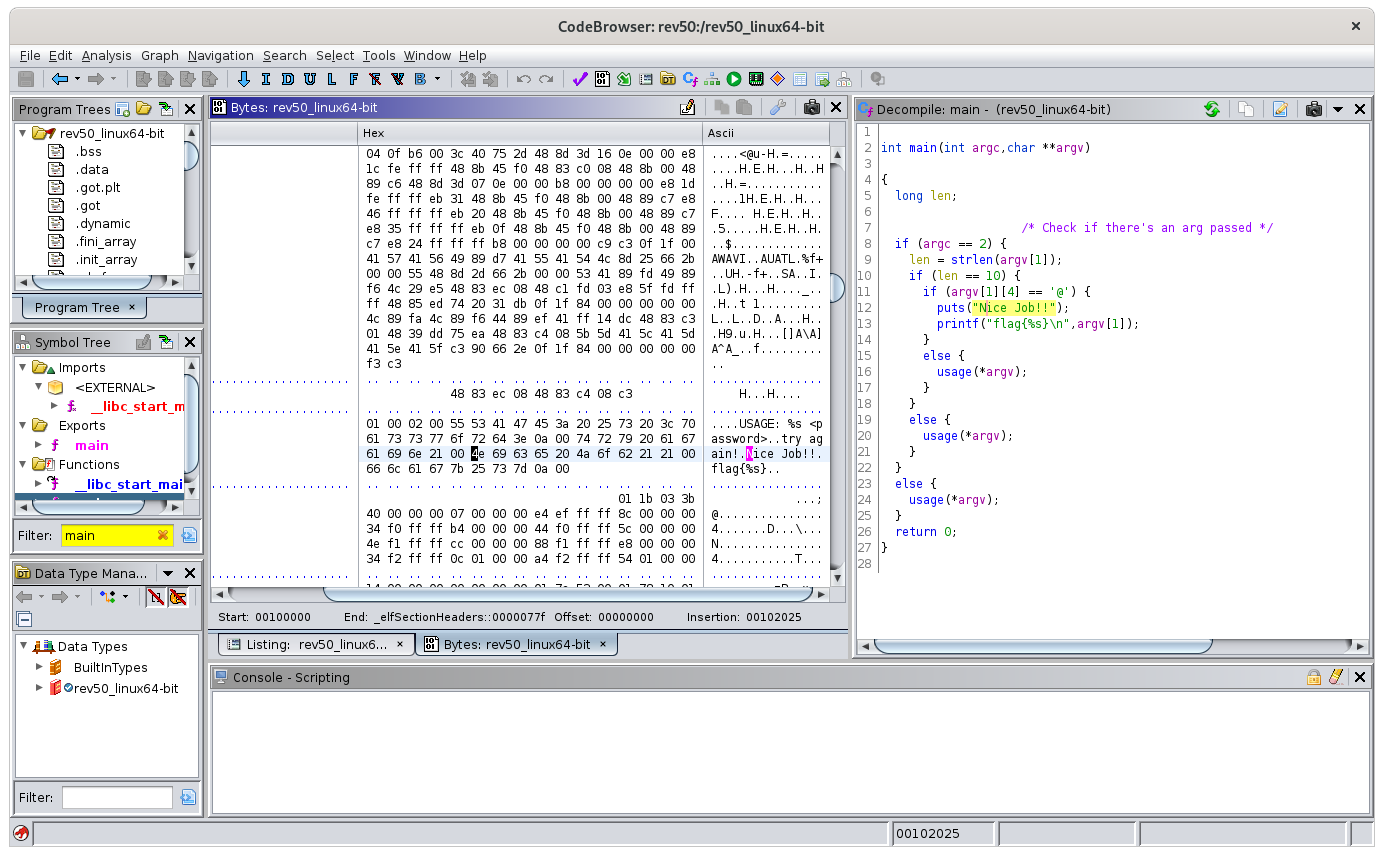
Ghidra is a software reverse engineering (SRE) framework. This framework includes a suite of full-featured, high-end software analysis tools that enable users to analyze compiled code.
Capabilities include disassembly, assembly, decompilation, graphing, and scripting, along with hundreds of other features. Ghidra supports a wide variety of processor instruction sets and executable formats and can be run in both user-interactive and automated modes. Users may also develop their own Ghidra plug-in components and/or scripts using Java or Python.
Permissions
3 permissions weaken the sandbox. Flatsonar asks before installing.
- X11 display: X11 lets apps read input and windows of other apps
--socket=x11 - full access to your home folder
--filesystem=home - development features (ptrace, can inspect other processes in its sandbox)
--allow=devel - inter-process communication (needed for X11)
--share=ipc - network
--share=network - audio
--socket=pulseaudio - GPU acceleration
--device=dri
Who publishes this
On Flathub: the manifest was reviewed and built on Flathub's infrastructure, but the developer has not verified ownership of the app id.
- installs a prebuilt binary instead of building from source
source:prebuilt - on Flathub: manifest reviewed and built by Flathub; the developer has not verified the app id
publisher:flathub
Maintenance
Recent activity on the upstream repository, or built and reviewed by Flathub.
No staleness signals: recent activity, or built and reviewed by Flathub.