
vmlinux-to-elf
by Marin M. - Fossplant.re
Convert raw Linux kernel blobs to ELF files
Broad permissions
Verified creator
GPL-3.0+
v1.3.6
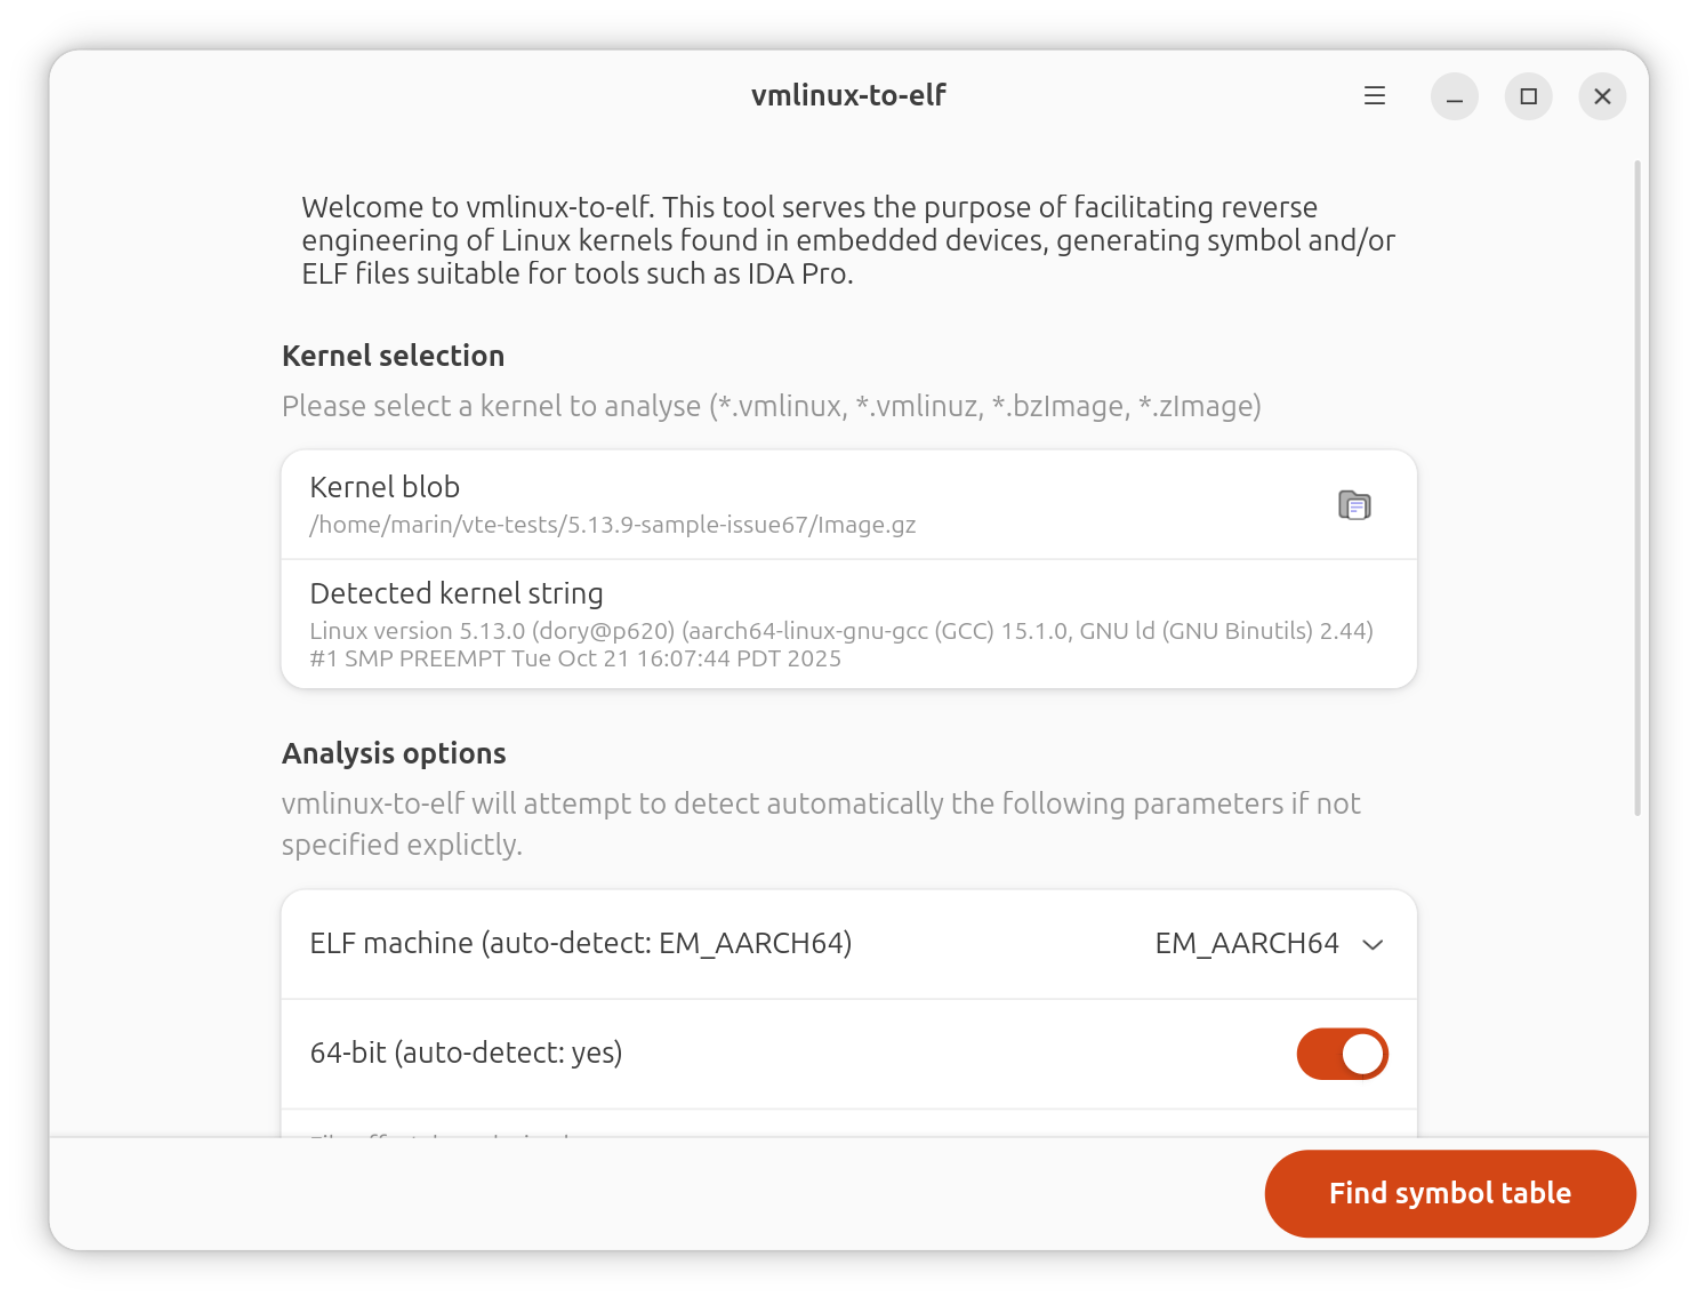
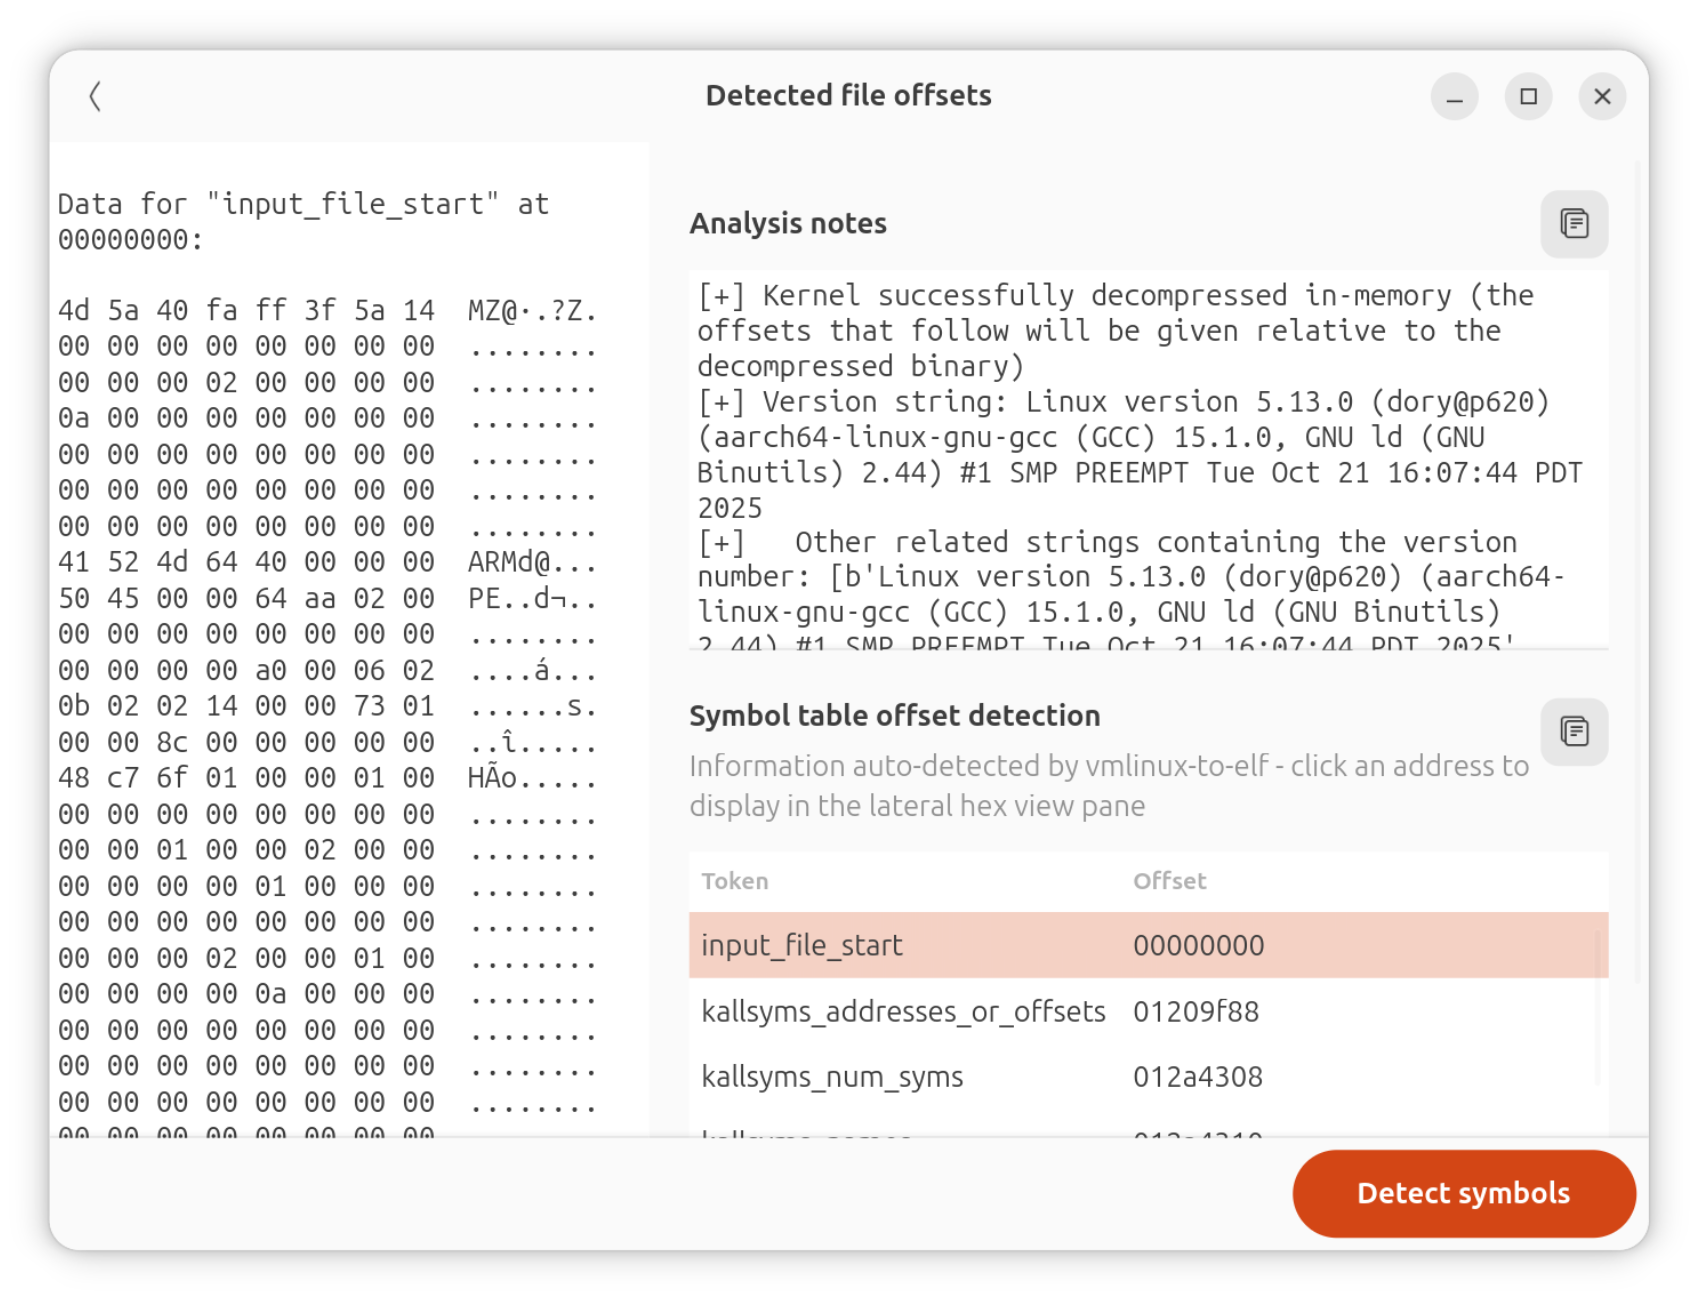
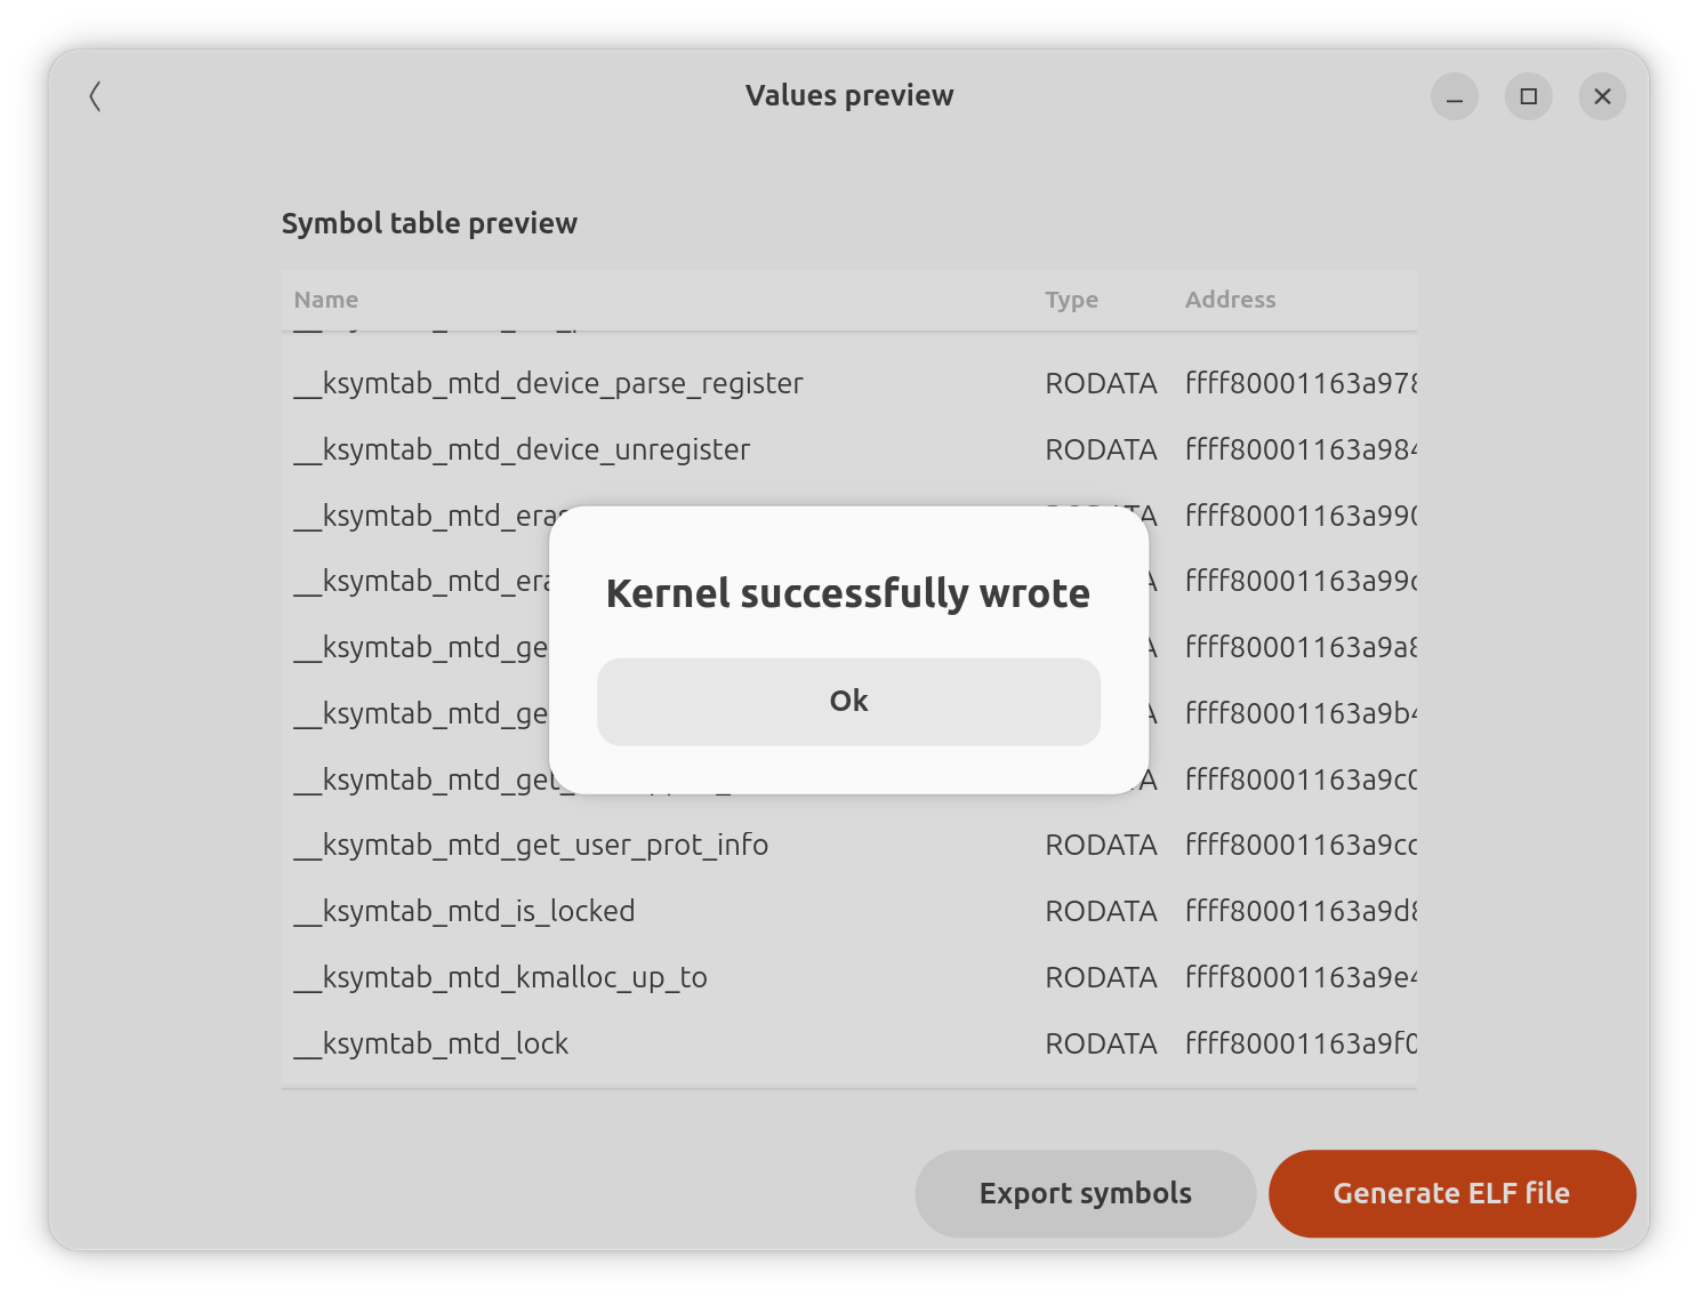
About
vmlinux-to-elf is a tool to recover a fully analyzable .ELF from a raw kernel, through extracting the kernel symbol table (kallsyms)
Features:
- Take a raw binary blob or ELF kernel file as an input.
- Automatically detect and unpack the main compression formats used for the Linux kernel.
- Find and extract the embedded kernel symbols table (kallsyms) from the input file.
- Infer the instruction set architecture, endianness, bit size, relying upon other things on common function prologue signatures.
- Infer the entry point of the kernel from the symbols contained in the kallsyms table.
- Provide basic inference for the kernel base address.
- Unpack certain types of Android boot.img files, starting with an "ANDROID!" or "UNCOMPRESSED_IMG" magic.
- Produce an .ELF file fully analyzable with IDA Pro or Ghidra as an output.
Permissions
1 permission weaken the sandbox. Flatsonar asks before installing.
- X11 display: X11 lets apps read input and windows of other apps
--socket=x11 - inter-process communication (needed for X11)
--share=ipc - Wayland display
--socket=wayland - X11 display, only when Wayland is unavailable
--socket=fallback-x11 - GPU acceleration
--device=dri
Who publishes this
The creator demonstrably controls this app id: Flathub verification, the hosting account owns the namespace, or a well-known file on their domain.
- verified on Flathub: the developer proved they control this app id
publisher:flathub
Maintenance
Recent activity on the upstream repository, or built and reviewed by Flathub.
No staleness signals: recent activity, or built and reviewed by Flathub.